Platform / The governance core
Controls
One control usually covers several risks. In a spreadsheet it is described several times, assessed several times and kept up to date in one place and not the others. Here it is maintained once, and a change reaches every risk it touches.
Drawn from the platform.
What changes
One control can cover four risks and be maintained once. Design and operating effectiveness are assessed separately, every assessment carries a date and an assessor and last year's judgement is still there when somebody asks what changed.
In detail
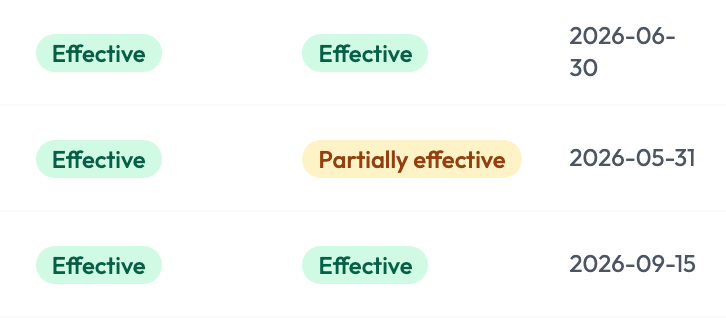
Controls sit in a library and link to the risks they mitigate, so a control that covers four risks is maintained once rather than four times, and a change to it reaches all four.
Controls are assessed through control self-assessment by the person who owns them, with an independent review by the second line where the framework calls for one, and the record says which kind each assessment was. Design and operating effectiveness are assessed separately, and every assessment stays on the record with a date and an assessor, so last year's judgement is still there when somebody asks what changed and why. An assessment that finds a control ineffective can raise a remediation action directly, so the finding and the response are linked from the start.
The evidence it leaves behind
Every assessment is a dated entry by a named assessor, and every change to a control writes to the audit trail. How the record is protected